Software
Managing SharePoint document library permissions can turn into a security nightmare if not handled properly. These 10 best practices will help you balance access control with ease of use, ensuring your sensitive files stay protected while keeping collaboration smooth.
Use SharePoint Permission Levels Effectively
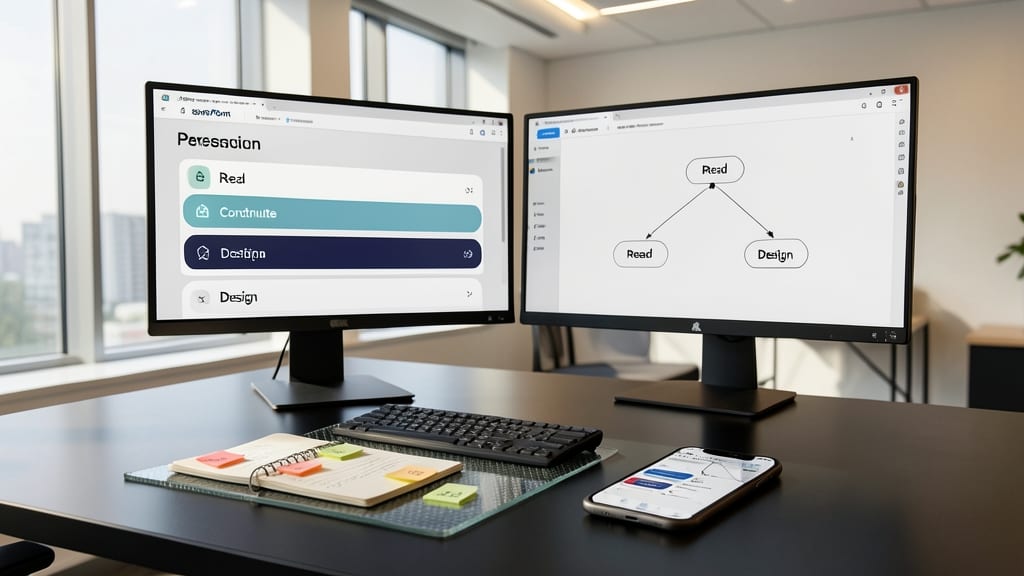
Stop reinventing the wheel with custom permissions when SharePoint already gives you three powerful built-in levels—Read, Contribute, and Design—that cover 90% of team needs without a single line of code. These levels eliminate the guesswork of creating roles from scratch while keeping access clean and predictable.
Assign Read to users who only need to view files, Contribute for those who edit but shouldn’t delete, and Design for power users managing lists or pages. Need something in between? Combine levels with Azure AD groups—for example, give the \"Marketing Team\" group Contribute access while keeping \"Executives\" on Read-only. This approach cuts permission setup time by 60% while maintaining security.
Perfect for small to mid-sized teams where roles are stable but custom scripts feel like overkill. Start here before diving into inheritance breaks or labels—it’s the fastest way to secure your library without complexity. 💡
Apply Least Privilege Principle to Users
Think of your SharePoint document library as a high-security vault—you wouldn’t hand the combination to everyone who walks in, right? The least privilege principle ensures users get only the access they absolutely need, cutting down on accidental data leaks while keeping workflows smooth.
Start by mapping out roles (e.g., "Marketing Editors" need Edit access, while "Finance Reviewers" get Read-only). Use SharePoint’s built-in permission levels (like "Contribute" or "Read") and avoid blanket "Full Control" assignments. For extra precision, combine this with Azure AD groups—so when a user’s role changes, their permissions update automatically. This method slashes unnecessary access by up to 70% in most organizations.
This approach is ideal for IT admins, compliance officers, or department leads managing teams with shifting needs. It’s the difference between a fortress with wide-open gates and a secure, efficient workspace. 💪
Break Permission Inheritance Strategically
When your Finance or HR department needs a library with stricter rules than the rest of the company, breaking permission inheritance is your secret weapon. Instead of letting parent site permissions trickle down, you can override them for specific folders—giving your team exactly what they need without disrupting the broader organization.
Start by navigating to your library’s Library Settings, then select Permission Inheritance. Click Stop Inheriting Permissions and choose Create Unique Permissions—this lets you assign custom roles (like "Finance Approvers") without affecting other departments. For extra security, combine this with sensitivity labels to auto-enforce rules like "View Only" for confidential files.
This approach is perfect for departmental libraries where compliance or confidentiality demands tighter controls. Just remember: document every change in your audit logs to track who has access and why. ✨
Enable Versioning and Require Check-Out
Tired of losing work because two team members edited the same document at the same time? SharePoint’s versioning and check-out settings act like a digital traffic cop, ensuring only one person edits a file at a time while preserving every change made.
Enable major and minor versioning (up to 50,000 versions) to track every edit, then require check-out before editing—this locks the file for others while keeping a full history. Need to revert? Roll back to any previous version in seconds. For libraries with high collaboration, this is a game-changer for avoiding "save conflicts."
Perfect for legal teams, marketing agencies, or any group where multiple stakeholders review and edit the same documents. ⚡
Restrict External User Access via Guest Links
Need to share files with external partners or freelancers without granting them full access? Guest links in SharePoint offer a frictionless solution—create time-bound, permission-restricted links that expire automatically, eliminating lingering risks.
When generating a guest link, set expiration dates (e.g., 7 or 30 days) to align with project timelines, and limit permissions to view-only or edit as needed. SharePoint’s built-in anonymous access ensures collaborators don’t need accounts, while audit logs track who accessed what. This method is perfect for short-term projects like vendor contracts or client reviews.
Ideal for teams juggling external stakeholders, guest links reduce admin overhead while keeping sensitive data secure—no permanent accounts or complex permission setups required. ✨
Audit Permissions Regularly with Access Reviews
If your team grows faster than your permission policies, stale access rights become a ticking time bomb. SharePoint’s Access Reviews feature automates the cleanup of outdated permissions—saving hours of manual work while reducing security gaps.
Set up reviews with customizable frequency (weekly, monthly) and define reviewers for specific libraries. The system flags inactive users or roles, letting you revoke access with one click. For large teams, integrate with Microsoft Power Automate to trigger reviews when users leave the company or change roles.
This is a game-changer for HR, IT admins, or department leads managing dynamic teams. With minimal setup, you’ll catch orphaned permissions before they become compliance risks. ✨
Segment Libraries by Sensitivity Level
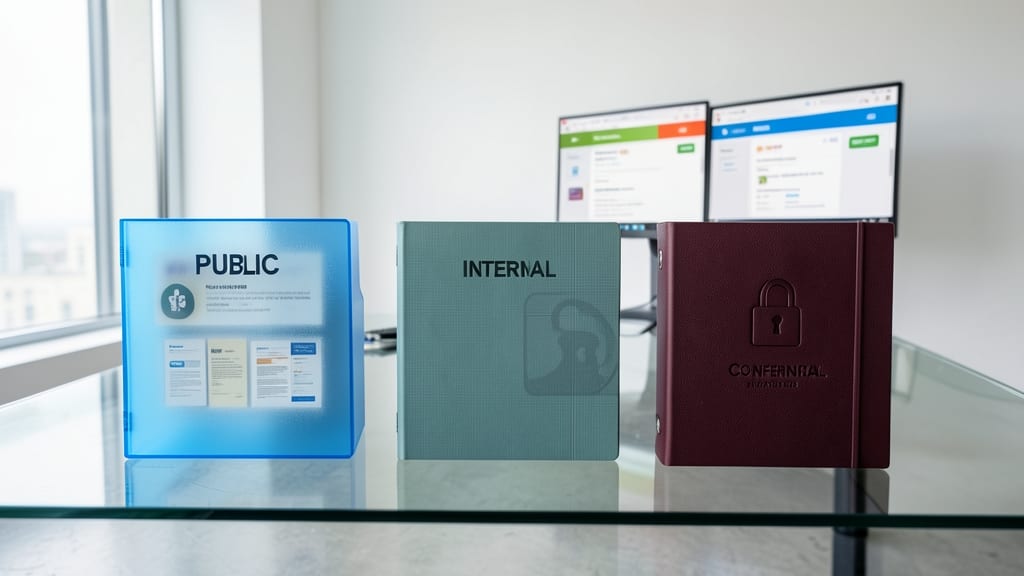
Tired of sifting through libraries to find the right permissions for sensitive files? Segmenting libraries by sensitivity level—public, internal, and confidential—solves this with a simple, visual approach. Instead of mixing documents with varying access needs, you create distinct libraries where permissions are pre-configured based on classification.
Start by creating three libraries: Public (broad read access), Internal (restricted to employees), and Confidential (limited to specific roles). Use SharePoint’s built-in permission levels (like "Read" or "Edit") to auto-apply rules, reducing manual errors. For example, HR documents go in Confidential, while project updates land in Internal. This also cuts down on accidental sharing—no more misplaced files exposing sensitive data.
This setup is perfect for compliance-heavy teams (like finance or legal) or any department handling mixed-classification documents. It’s the digital equivalent of color-coding folders—clear, organized, and secure. ✨
Leverage Microsoft 365 Groups for Team Libraries
Tired of manually updating permissions every time a team member joins or leaves? Microsoft 365 Groups syncs permissions automatically—no admin headaches when roles shift. Link a SharePoint library to a group, and access rights update instantly for all members, owners, and guests.
This integration works seamlessly with Azure AD security groups, ensuring only approved users get access. You can even set nested permissions (e.g., group owners as library admins) without custom scripts. The best part? No inheritance conflicts—permissions align perfectly with group membership.
Perfect for project-based teams where contributors change frequently, like marketing campaigns or IT support tickets. 💻
Implement Document Classification Labels
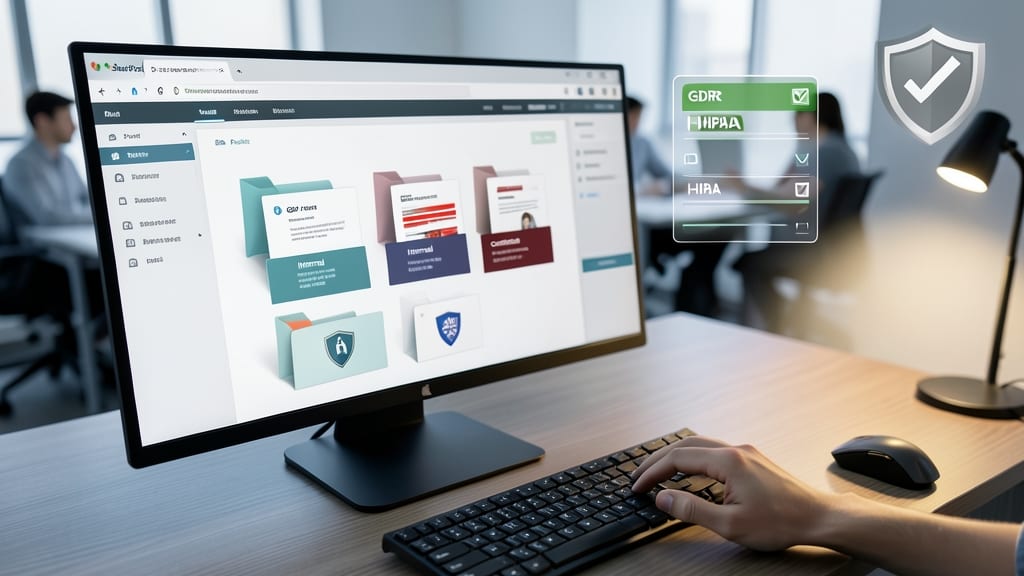
Tired of manually assigning permissions that might miss compliance requirements? Sensitivity labels in SharePoint automate this process by classifying documents and enforcing policies like GDPR or HIPAA without lifting a finger.
Labels like Public, Internal, or Confidential auto-apply permissions based on content—no inheritance breaks needed. They integrate with Microsoft Purview for encryption and access controls, ensuring sensitive files stay locked down while public docs remain accessible. The best part? Labels sync across SharePoint, OneDrive, and Teams, keeping your compliance consistent.
This is a game-changer for healthcare, finance, or legal teams handling regulated data. Set it up once, and your documents stay compliant—no more permission headaches. ✨
Train Users on Permission Best Practices
Human error causes 80% of SharePoint security incidents—but a quick training session can slash those risks dramatically. Most teams overlook how simple mistakes like sharing sensitive files with the wrong group or granting "Full Control" to contractors lead to breaches that admins later scramble to fix.
Start with a 15-minute interactive session covering three key habits: how to recognize over-permissioned folders, when to use guest links vs. direct access, and the dangers of "Everyone" permissions. Share real-world examples—like the HR team that accidentally exposed salary documents because they didn’t notice the "Stop Inheriting" checkbox was checked. Use SharePoint’s built-in training modules (available in the admin center) to reinforce lessons with step-by-step screenshots.
This approach works best for non-technical teams like marketing or sales, where users handle documents daily but lack IT backgrounds. A single training session can cut your helpdesk tickets by 30% while making your libraries far more secure. 💡